Apple patches high-severity eavesdropping vulnerability in Beats Studio Buds
The vulnerability, disclosed 12 months ago, affects multiple manufacturers.
The vulnerability, disclosed 12 months ago, affects multiple manufacturers.
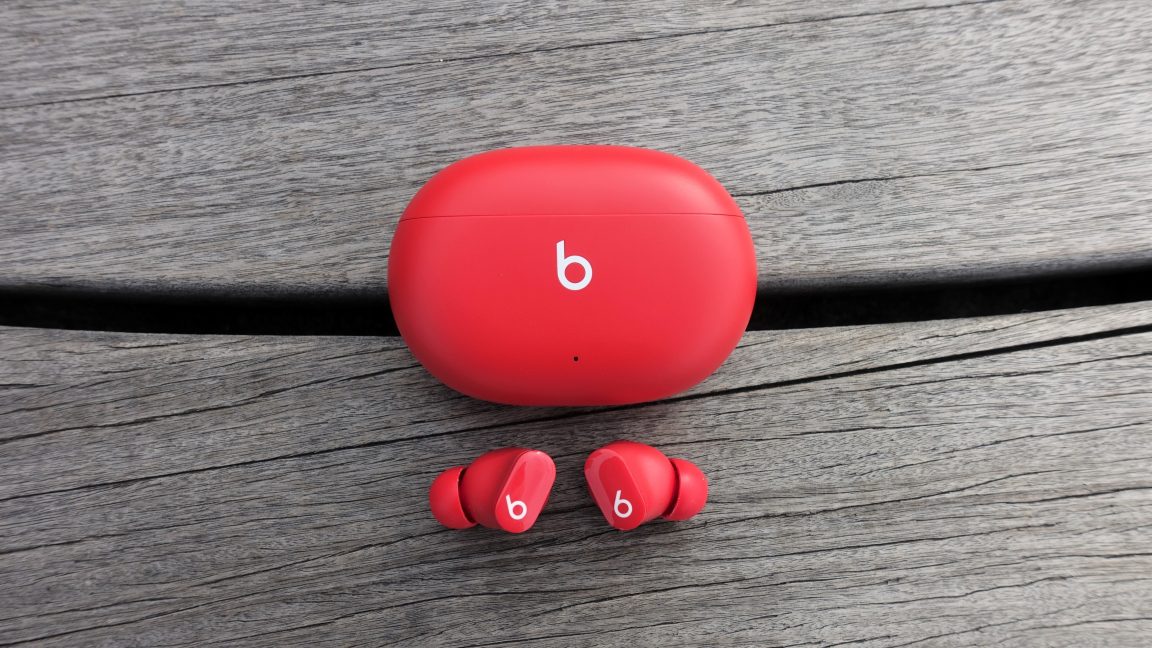
Apple has updated its Beats Studio Buds wireless earbuds to patch a high-severity vulnerability that could be exploited by nearby hackers to eavesdrop on users.
The vulnerability, CVE-2025-20701, allowed improper authentication in the firmware running on the Bluetooth-related chips, enabling people within signal range to impersonate devices that had previously been paired with the earbuds. The researchers demonstrated this in a series of end-to-end attacks that allowed them to eavesdrop on conversations or sounds within earshot of the phone microphone.
“Impact: An attacker within Bluetooth range may be able to listen through the microphone of a device which is not yet paired and actively seeking pair requests,” Apple said in a Tuesday security advisory. The fix is contained in Beats Firmware Update 1B211, which is delivered automatically while headphones are paired with and within Bluetooth range of a user’s iPhone, iPad, or Mac. Users can check their firmware version by going to Settings on their device, navigating to Bluetooth, and tapping the info button next to the headphones.
This story was first published by Ars Technica. Read the original report
We use cookies to run this site and, with your consent, to measure traffic and improve our content. Necessary cookies are always on. You can accept all cookies or choose which ones to allow. Privacy policy.