New bootloader lets you take the "Meta" out of the original Meta Quest
Privilege escalation attack grants "full control" and freedom from Meta's servers/apps.
Privilege escalation attack grants "full control" and freedom from Meta's servers/apps.
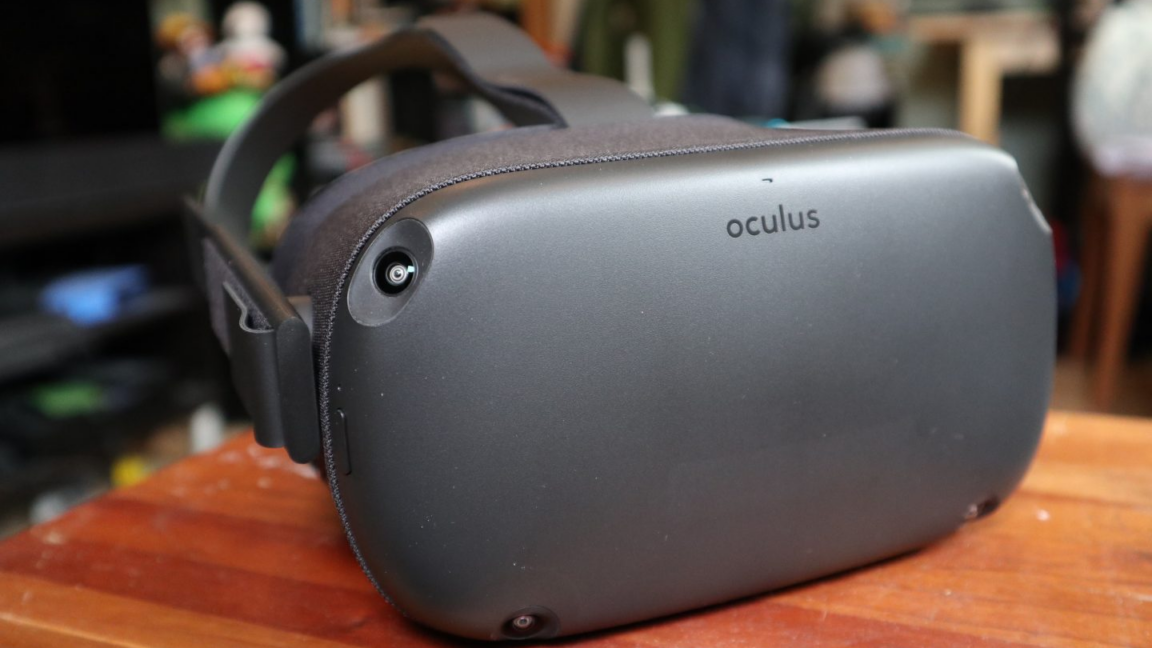
Remember the original Quest headset that Meta (then Oculus) trumpeted back in 2019? Meta seems to hope you don't, since the company officially stopped supporting the wireless VR headset in 2023 to focus on the more popular Quests 2 and 3. Luckily, tinkerers haven't similarly abandoned the hardware and recently released a new root-access exploit and bootloader that gives "developers and enthusiasts full control over Quest 1 hardware."
The QuestStack project integrates previously known vulnerabilities in the Quest's Android fastboot process into a privilege escalation chain that leads easily to full root access on the device. The bootloading process is now streamlined enough that it can be completed without any downloads through a web interface after connecting the headset to a PC.
With this exploit, the original Quest hardware can now be officially divorced from any reliance on Meta's servers or services to be useful. That means enterprising Quest owners should be able to sideload apps without needing to register for a Meta Developer account and activating Developer Mode through Meta's mobile app. It also means users should be able to go through the initial setup and login steps for a fresh Quest headset even if and when Meta decides to shut down the servers that currently support this process.
This story was first published by Ars Technica. Read the original report
We use cookies to run this site and, with your consent, to measure traffic and improve our content. Necessary cookies are always on. You can accept all cookies or choose which ones to allow. Privacy policy.